

The ten-million-dollar invisible man
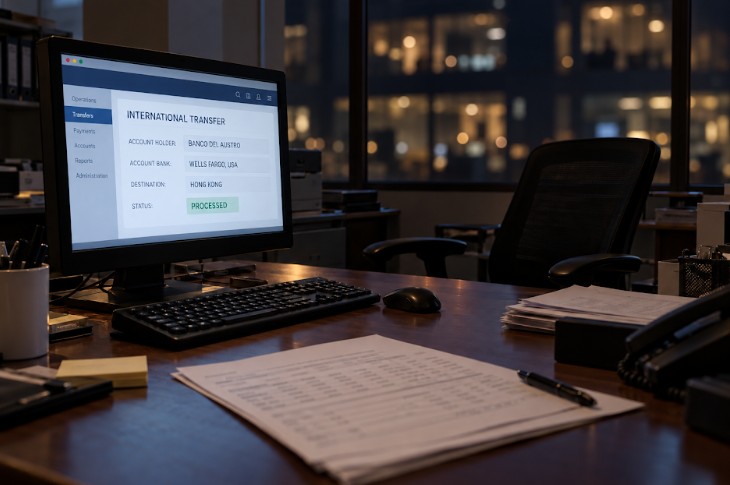
Shortly after seven on a January evening in 2015, a computer at Banco del Austro sent an instruction to Wells Fargo in the United States to the effect: “Send lots of money to Hong Kong and Dubai!”
Since it appeared to have the proper credentials, Wells Fargo acted on it.
Over the following ten days, at least twelve transfers moved approximately $12 million out of Banco del Austro’s account. There was no masked man at the counter, no getaway car outside and no cashier pressing a concealed alarm. The instruction arrived through SWIFT, the international messaging network banks use to tell one another where money should go.
 Unfortunately, the people giving the instructions were bank robbers.
For those of us accustomed to seeing Banco del Austro as part of the ordinary scenery of Cuenca, this introduces an unexpected international dimension. Behind the familiar business of paying bills and withdrawing cash lay a story involving American bankers, Hong Kong companies, stolen computer credentials and, ultimately, suspicions about North Korean hackers.
Quite a lot of geography for a robbery conducted from behind a desk.
The thieves had somehow obtained a Banco del Austro employee’s SWIFT login credentials. They retrieved previously cancelled or rejected payment requests, changed the amounts and destinations, and resubmitted them. It was more than a week before the bank noticed the money was missing, which must have created a great deal of alarm.
The results of the investigation into how the credentials were obtained, and whether anyone inside knowingly assisted, has never been made public. The use of an employee login shows that someone acquired access, but doesn’t prove that any employee had anything to do with the robbery.
As one might suspect, Banco del Austro and Wells Fargo subsequently presented rather differing views of responsibility. The Ecuadorian bank argued that unusually large transfers, requested outside normal business hours, should have automatically waved a red flag. Wells Fargo maintained that it had acted on authenticated instructions and laid the blame squarely on security failures at Banco del Austro.
One can see the difficulty here. If a stranger arrives with your keys, the fact that the keys fit the lock to your apartment does not make him the owner. On the other hand, the person who let the keys fall into the stranger’s hands may also have some explaining to do.
Following the money produced another chapter in the story, although not a complete solution.
Court documents examined by Reuters news agency showed that approximately $9.14 million reached accounts belonging to four Hong Kong companies and that a further $2.8 million arrived at accounts in Dubai and Los Angeles. Some of it then moved through nineteen additional companies. A judge described the first four recipients as apparently inactive corporate vehicles controlled by mainland Chinese citizens.
None of them were businesses Banco del Austro recognized as customers or trading partners. The bank pursued recovery proceedings in Hong Kong, obtained account freezes and did eventually reach some settlements.
There was, then, a money trail, but finding the companies through which stolen money passed is not necessarily the same thing as finding the people who organised the theft.
And what about North Korea? The Ecuadorian theft has been associated with the broader story of Lazarus and APT38, names used by cybersecurity researchers for North Korean hacking operations, including sophisticated bank robberies.
However, suspicion is not proof. In its 2018 report, the security firm Mandiant discussed Banco del Austro among suspected incidents but could offer only limited insight into this particular attack.
So North Korea remains under suspicion in this case, but there is no firm evidence.
The American lawsuit supplied an ending of sorts. In February 2018, Banco del Austro and Wells Fargo settled out of court. Reuters reported that the settlement discussions were sealed and the financial terms were not disclosed. Of course they weren’t.
There was never a public verdict assigning responsibility between the banks, and no publicly confirmed settlement figure telling us how much Banco del Austro recovered from Wells Fargo.
The lawyers could close their files, but anyone else hoping for the final denouement of a detective story was left looking at a locked drawer in a filing cabinet.
Could something like this happen again? Yes, possibly. But that does not mean Banco del Austro is about to suffer another identical robbery, or that banking security has stood still since 2015.
SWIFT now operates a mandatory Customer Security Programme, with security controls for participating institutions and a framework for independent assessments. There are considerably more formal safeguards than the old notion that an authenticated message must be a legitimate instruction.
Nevertheless, criminals still exploit the gap between an instruction that looks genuine and one that actually is genuine. The FBI continues to warn about business e-mail compromise, in which fraudulent or compromised communications persuade people to send money to the wrong account.
This is different from this particular bank theft, but it exploits a similar weakness in that someone trusts the apparent authority of a message.
For the ordinary resident of Cuenca, the useful lesson is not to spend the afternoon worrying about North Korean agents standing behind ATMs disguised as street sweepers. It is to pause for a moment when a familiar supplier suddenly announces new bank details, or an urgent message asks for an unexpected transfer. Confirming the request by voice through a phone or Whatsapp call with a contact you already know is always a good idea.
The Banco del Austro affair remains a mystery with several answers missing from public view. We know the method, parts of the money trail and how the dispute between the banks ended, but we don’t have a complete account of who organized the heist or who ultimately absorbed every dollar of the loss.
The missing money did travel around the world, but the question of whodunnit remains a mystery.